Retail · Wholesale · Distribution
Optimising Retail Operations
Connect every store to HQ and cloud applications such as SAP on Azure over one encrypted network, with QoS for billing, inventory and reconciliation traffic.
ChiefNET SD-WAN · NGFW
A cloud-native SD-WAN that unifies headquarters, branch offices, data centres, public clouds and remote workers into one secure network, with a single physical or virtual device per location.
Architecture
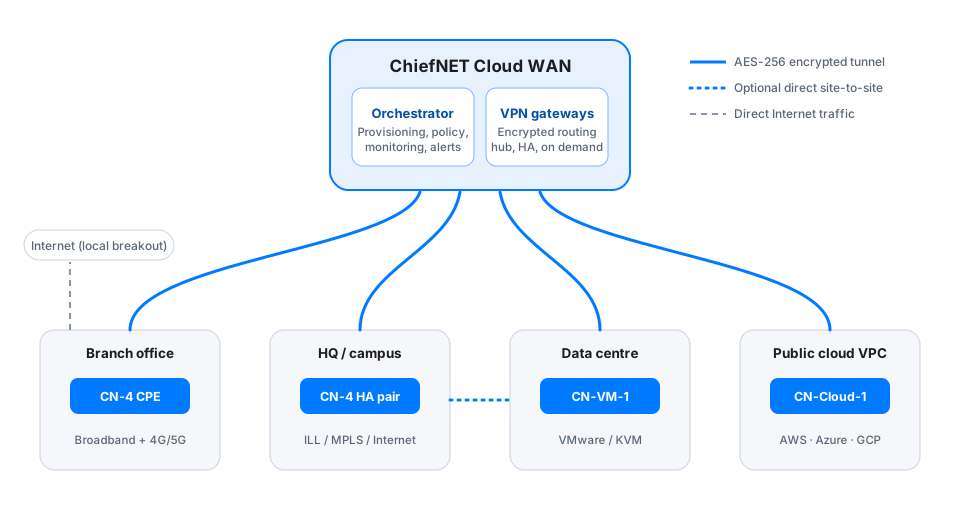
Every customer network is pre-provisioned with secure site-to-site connectivity and access to data centres and cloud services. Expanding to a new site means shipping one device.
The centralised management and policy engine. One console to configure, provision, monitor and troubleshoot the entire network, with zero-touch provisioning and automated policy enforcement across every site.
A physical, virtual or cloud appliance at each branch, HQ, data centre or VPC. Pre-provisioned at the factory, so it can be installed without technical expertise on site.
Encrypted VPN gateways launched on demand as containers in data centres close to your sites. Every customer network is isolated and gets site-to-site and site-to-cloud connectivity automatically.
Capabilities
Routing, security, QoS and high availability in one device, managed from one console.
Security
All data, management and monitoring traffic is encrypted, and every device is authenticated before it joins the network. For content-level inspection, ChiefNET integrates per CPE with Palo Alto Networks Prisma Access.
AES-256-GCM with SHA-256 over TLS-based tunnels. Every customer network is isolated from every other.
Each CPE authenticates with X.509 certificates unique to the deployment, rotated automatically.
Hardened Linux with long-term support. Local access is disabled, and all WAN ports are blocked by default.
Management over HTTPS only, with two-factor authentication. Remote diagnostics run over SSH from the ChiefNET side.
ChiefNET never inspects customer traffic. Keys are negotiated dynamically with public-key authentication.
Hardware-independent software runs on multiple vendor platforms, so supply issues never block a deployment.
Deployment options
Pick the topology that fits your utilisation, compliance and growth plans, and change it later without re-architecting.
Orchestrator and Cloud WAN gateways run in the ChiefNET cloud, pre-provisioned for your enterprise. No CapEx at HQ or the data centre.
Orchestrator, gateway and controller installed on your own servers with high availability, for full control and data residency.
Mix and match: on-prem preferred with cloud fallback, for example to ride through optical LAN outages between buildings.
CPE models
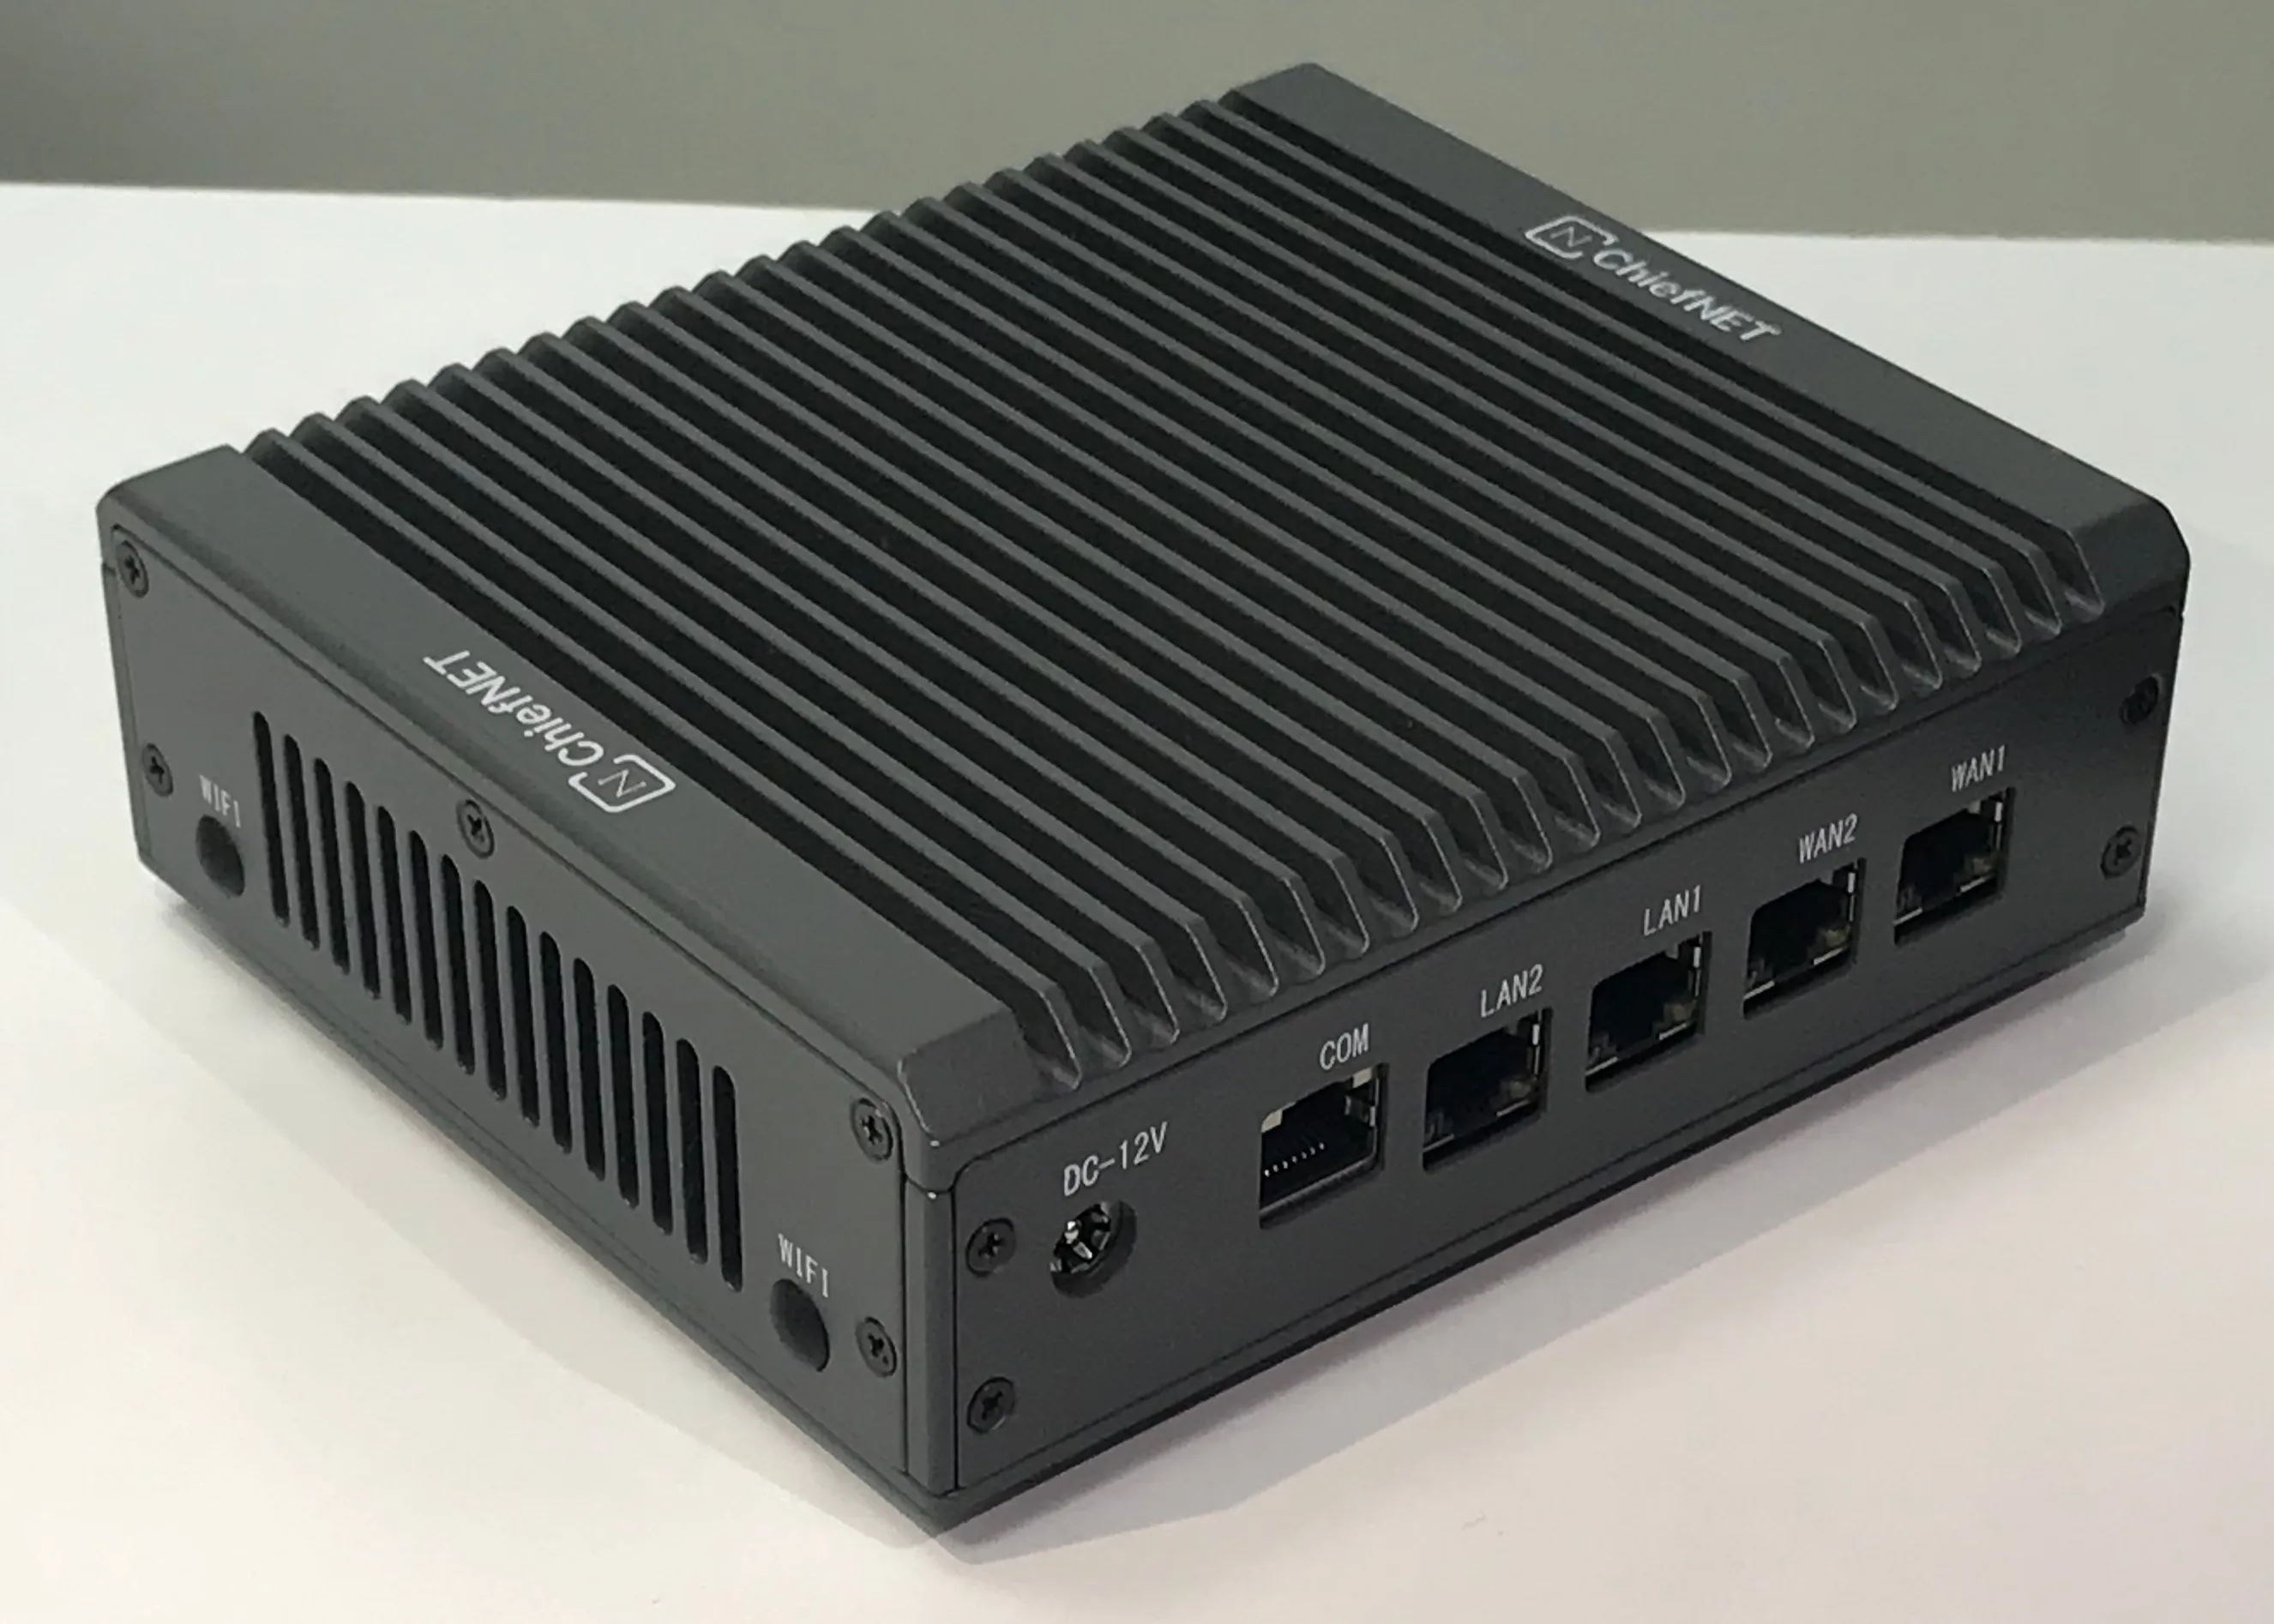
Open and hardware independent: ChiefNET runs on standard x86 and ARM hardware and on all major virtualisation and cloud platforms.
| Model | CN-4 | CN-IOT-1 | CN-VM-1 | CN-Cloud-1 |
|---|---|---|---|---|
| Type | Hardware appliance | IoT / edge device | Virtual CPE (on-prem DC) | Cloud CPE |
| Platform | Intel x86_64, 4-core CPU, 8 GB RAM, 120 GB NVMe | Raspberry Pi, custom enclosure | x86_64 virtual machine | x86_64 virtual machine |
| Ports | 4 × 2.5 GbE; optional optical, LTE/5G, Wi-Fi | 1 × GbE, Wi-Fi | 4 × virtual Ethernet | 4 × virtual Ethernet |
| WAN / Internet throughput | 2.5 Gbps | 50 Mbps | Up to 1 Gbps (host dependent) | Up to 1 Gbps (instance dependent) |
| WAN / VPN throughput | 800 Mbps | 5 Mbps | 200 Mbps | 200 Mbps |
| Deployment | Commercial, SOHO, retail, industrial | Commercial, SOHO, residential, IoT | VMware or KVM | AWS, Azure, GCP, DigitalOcean |
| Power | 110/220 V adapter, 60 W max | Adapter, 20 W max | N/A | N/A |
| Recommended users | 100 | 5 | 150 | 150 |
| Interfaces | 4 Ethernet ports (2 LAN, 2 WAN by default; 2.5 GbE on CN-4), optional LTE/5G |
|---|---|
| VLAN tagging | IEEE 802.1Q on all ports |
| Bridging | Yes, as LAN or as WAN |
| Routing | OSPF, BGP, static routes, policy-based routing |
| WAN failover | Yes, quality-based with link-quality monitoring |
| WAN load balancing | Yes, weighted; simultaneous with failover |
| Supported devices | Physical CPE (several models), virtual CPE (VM), cloud CPE on all major public clouds |
| Autonomous offline mode | Yes, devices keep operating without contact with the orchestrator |
| Application-aware networking | Application-DNS maps, application-based steering, domain-based QoS |
| NAT / PAT / NAPT / DNAT | Yes |
| SASE / SSE / Zero-Trust | Integration with leading SASE vendors |
| Mechanism | Fine-grained hierarchical QoS with fair sharing, guarantees and limits |
|---|---|
| Minimum bandwidth guarantee | Yes |
| Maximum bandwidth limit and shaping | Yes, including per-port limits |
| Low-latency / real-time QoS | Yes |
| Application-specific QoS | Yes, by domains and application groups |
| 5-tuple QoS | Yes |
| Enterprise tunnel QoS | Yes, integrated with WAN QoS, load balancing and failover |
| Sensitive-traffic exclusive forwarding | Yes |
| Orchestration platform | Cloud hosted or installed on premises |
|---|---|
| Orchestrator access | Web browser over HTTPS (HTTP redirected) |
| Traffic isolation | Each customer's traffic isolated and encrypted |
| Multi-tenancy | Each customer views only its own devices |
| CPE operating system | Hardened OS with long-term support |
| CPE local access | Disabled to prevent unauthorised access |
| Encryption | AES-256, SHA-256, SHA-512 |
| CPE WAN security | Outbound only by default; all WAN ports blocked; verified with NESSUS/NMAP |
| DNS | Split-horizon DNS with enterprise DNS preference |
| Traffic filters | 5-tuple filtering, DNS-based domain filtering, application filtering |
| Access levels | Full admin, read-only admin, read-only limited user, multi-org admin |
|---|---|
| Authentication | Username and password with two-factor authentication |
| Zero-touch provisioning | Yes, no skilled personnel needed on site |
| Remote troubleshooting | Yes, over SSH from ChiefNET sites |
| Remote software upgrade | Yes, automatic updates for all devices |
| Dashboards and data collection | Grafana portal, cloud hosted or on customer servers |
| Reports and alerts | Custom SLA, WAN and device availability reports; real-time alerts by email and Telegram |
| Vulnerability assessment | Periodic WAN-side vulnerability assessment report |
Application notes
Read each note online or download it as a PDF.
Retail · Wholesale · Distribution
Connect every store to HQ and cloud applications such as SAP on Azure over one encrypted network, with QoS for billing, inventory and reconciliation traffic.
Retail · Manufacturing · Warehousing
View live and recorded video from any site without opening camera or NVR ports to the Internet, using ChiefNET's encrypted private network.
Healthcare · Diagnostics
Link hospitals, clinics and labs to HIS, EHR and PACS in the data centre or cloud over an encrypted, highly available network with QoS for imaging.
Manufacturing · Industrial
Interconnect plants, remote monitoring stations and offices so MES, ERP and monitoring traffic flows securely and predictably between every site.
Cross-industry · Enterprise IT
Extend one encrypted network from branches and VMware or KVM data centres into AWS, Azure, GCP and DigitalOcean with ChiefNET virtual and cloud CPEs.
Retail · Financial services · Distributed enterprises
Keep branches online through ISP and device failures with link-quality monitoring, failover, weighted load balancing, VRRP and protected 4G/5G backup.
Cross-industry · Regulated enterprises
Secure branch Internet access with ChiefNET's network firewall and DNS filtering, and add Palo Alto Networks Prisma Access for content security per site.
ISPs · MSPs · MSSPs
Run managed SD-WAN for many customers from one account, with SLA reports that separate device, power and ISP outages, plus Grafana, Splunk and Zoho integration.
Utilities · Telecom · Banking · Retail
Connect small, unmanned sites over LTE or 5G with zero-touch CN-IOT-1 devices, private access to IoT equipment and no open ports.
Architecture, features, specifications and CPE models (CN-4, CN-IOT-1, CN-VM-1, CN-Cloud-1).
One-page overview of core capabilities, security and device models.
How ChiefNET uses the Internet as the enterprise core: VPN, QoS, firewall, steering and breakout.
Provisioning, access control, hardened CPE, encryption, isolation and supply-chain protection.
Configuration guides and feature references are in the ChiefNET product documentation.
We offer customised product demonstrations and pilot deployments. Tell us about your sites and applications.