Executive Summary
Industrial Control Systems (ICS) – the DCS, PLCs, SCADA and safety systems that run manufacturing lines, process plants, water treatment works and other industrial facilities – were engineered for deterministic, always-on operation, not for defending against network-borne intrusion. As manufacturers pursue Industry 4.0 initiatives – connecting the plant floor to MES, enterprise historians and cloud analytics – every new connection widens the path an attacker could use to reach the control system itself.
ChiefNET OT Shield is a hardware-enforced data diode purpose-built to close that gap. It allows process values, batch data, historian records and equipment telemetry to flow out of the ICS network to enterprise IT and cloud systems, while making it physically impossible for any command, malware or intrusion attempt to flow back in. There is no firewall rule to misconfigure and no firmware to patch under production change windows; isolation is built into the hardware itself.
This document presents a use-case-driven view of how ChiefNET OT Shield applies to industrial control system environments across discrete manufacturing, process industries and critical utilities – covering reference architecture, detailed use cases, standards alignment, and the business case for plant-wide and multi-site deployment.
Industry Context: Cybersecurity Challenges in Industrial Control Systems
Convergence of IT and OT on the Plant Floor
Modern plants increasingly integrate MES, enterprise historians, predictive maintenance analytics and remote vendor support directly with PLCs, DCS and SCADA systems. This IT/OT convergence delivers real operational benefits – higher overall equipment effectiveness (OEE), faster troubleshooting, and data-driven maintenance – but it also means that a compromised laptop, VPN credential or unpatched firewall on the IT side can become a direct path into process control.
A Well-Documented Threat History
ICS-targeted malware has a well-established track record: Stuxnet demonstrated in 2010 that malware could be engineered to manipulate PLC logic and physically damage equipment; more recent ransomware campaigns against manufacturers have repeatedly caused multi-week production shutdowns by moving laterally from IT networks into OT networks that were assumed to be segmented. National ICS security agencies continue to issue advisories on vulnerabilities in widely deployed PLC, HMI and historian products, underscoring that the exposure is ongoing rather than historical.
Why General-Purpose IT Security Falls Short
-
Firewalls and VPNs are software-defined and bidirectional by design – a misconfigured rule, an unpatched CVE, or a stolen credential can open a path back into the control network.
-
Patch cycles that are routine in IT are disruptive in ICS, where planned maintenance windows may be months apart and unplanned downtime directly costs production.
-
ICS protocols (Modbus, OPC, EtherNet/IP, Profinet) were designed for engineering reliability, not authentication or encryption, making protocol-level attacks difficult to detect with IT-centric tools.
-
Many plants have flat, legacy control networks where a single foothold can reach multiple lines or cells.
Regulatory and Standards Drivers
Industrial operators are increasingly expected to demonstrate structured OT security controls, whether through regulation, customer contract requirements, or insurance underwriting:
-
IEC 62443: the leading international standard for Industrial Automation and Control System (IACS) security, structured around security levels and zone/conduit segmentation – a model a hardware data diode implements directly as a one-way conduit.
-
NIST SP 800-82: US guidance for ICS security that explicitly recommends unidirectional gateways at the boundary between control networks and corporate/enterprise networks for high-consequence systems.
-
Purdue Model (ISA-95): the reference architecture used across manufacturing to define levels 0-5; a data diode is a natural fit for the Level 3/3.5 to Level 4 boundary where OT data is exported without opening a path back down.
-
CERT-In & Sectoral CERT Advisories (India): reinforce baseline security hygiene and incident-reporting obligations for critical and industrial information infrastructure operators.
-
Customer & Insurance Requirements: increasingly reference OT/IT segmentation as a condition of cyber-insurance coverage and as a due-diligence item in supply-chain security questionnaires.
ChiefNET OT Shield: Solution Overview
ChiefNET OT Shield is a purpose-built OT cybersecurity appliance combining a hardware-enforced data diode with a hardened, cloud-managed communications platform. It is designed to sit precisely at the boundary between the plant’s control network and the enterprise IT, MES or cloud systems that need visibility into it.
Core Architecture
-
Physical transmitter (TX) module on the secure/restricted side and a physically separate receiver (RX) module on the monitoring/enterprise side, joined only through an optical, one-way link.
-
No physical mechanism exists for signals to travel from the RX side back to the TX side – isolation is enforced by hardware, not by a rule set that can be disabled or bypassed.
-
A hardened operating system on both sides minimises attack surface and removes the general-purpose services that create most software vulnerabilities.
Key Capabilities
-
Native ICS protocol support: BACnet, Modbus, MQTT, OPC UA and industrial UDP (broadcast/multicast/anycast), covering common PLC, DCS and building/plant automation telemetry.
-
File and log transfer: UDP file transfer, Syslog and HTTP PUT for historian exports, batch reports and equipment event logs.
-
Encrypted VPN transport: data exiting the diode is carried to MES, enterprise historian or cloud endpoints over a hardened, encrypted tunnel, without reopening a return path.
-
Dual WAN / 4G-5G failover: on the monitoring (RX) side, ensuring uninterrupted delivery of plant telemetry even where fixed-line connectivity is unreliable.
-
Built-in SD-WAN functionality: for manufacturers with multiple plants, enabling secure interconnection of sites with head office while keeping each plant’s OT network isolated.
-
Centralised cloud orchestration: zero-touch and pre-provisioning, fleet-wide monitoring, alerting and dashboards – essential for multi-plant manufacturers.
-
Zero patch burden: because isolation is physical rather than rule-based, there is no firewall ruleset or reverse-path exploit to patch against – reducing the outage-prone patch cycles that plague OT firewalls.
Reference Architecture
Single-Site Deployment – Plant / Process Control
At a single plant, ChiefNET OT Shield sits between the OT zone (DCS/PLC/SCADA, historian, safety instrumented system, field instrumentation) and the IT zone (MES, enterprise historian, cloud dashboards, corporate SOC). All operational data leaves the OT zone through the diode’s transmitter; nothing – no command, no query, no malware – can traverse back.
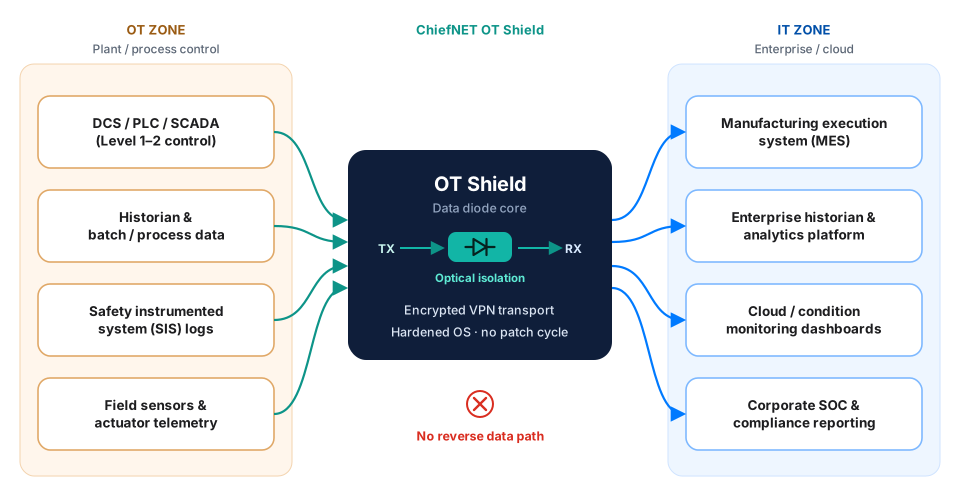
Single-site reference architecture – unidirectional OT-to-IT data flow via ChiefNET OT Shield
Multi-Plant / Fleet-Wide Deployment
Manufacturers operating multiple plants, cells or process units can deploy one OT Shield per site, provisioned and monitored from a single cloud console, while each site’s isolation guarantee remains entirely local and independent – a compromise or outage at one plant cannot propagate to another.
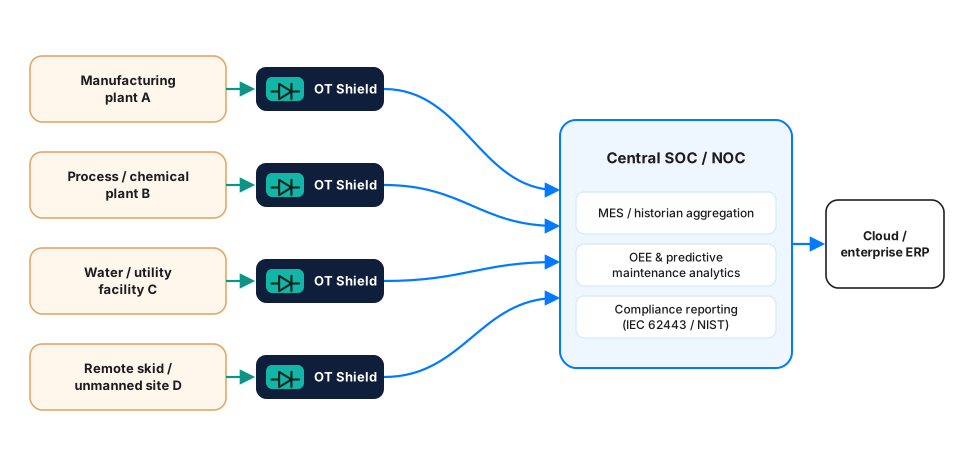
Fleet-wide deployment – multiple plants converging on a central SOC/NOC and enterprise systems
Detailed Use Cases
The following use cases illustrate how ChiefNET OT Shield is applied across discrete manufacturing, process industries and industrial utilities.
MES / Enterprise Historian Data Replication
Discrete & Process Manufacturing
- Challenge
- Manufacturing Execution Systems (MES) and enterprise historians need real-time visibility into PLC/DCS process values and batch data for OEE tracking and quality reporting, but the control network must remain isolated from corporate IT to protect production-critical logic.
- OT Shield solution
- OT Shield taps the plant historian and key PLC/DCS points on the secure TX side and replicates them one-way to the MES or enterprise historian on the IT side over an encrypted VPN, using OPC UA / Modbus protocol support – with zero possibility of write-back to the control network.
- Outcome
- Real-time OEE and production visibility without touching the control network
- Quality and batch reporting enabled without re-architecting the ICS
- Control network remains fully air-gapped from any external network path
Predictive Maintenance & Condition Monitoring
Rotating Equipment & Critical Assets
- Challenge
- Reliability teams want vibration, temperature and equipment health data from field instrumentation to feed predictive maintenance analytics, but the instrumentation network sits inside the same zone as safety and control systems.
- OT Shield solution
- OT Shield forwards sensor and equipment telemetry one-way to a cloud or on-premise predictive maintenance platform, supporting UDP and OPC UA feeds without exposing the underlying control or safety network.
- Outcome
- Reduced unplanned downtime through early fault detection
- Analytics platform receives continuous telemetry with no OT exposure
- Scales across multiple lines without additional attack surface
Legacy PLC / SCADA Modernisation Without Re-engineering
Brownfield & Ageing Plants
- Challenge
- Many plants run legacy PLC and SCADA platforms that cannot be easily upgraded, yet management wants modern dashboards and cloud analytics without re-architecting or re-certifying the underlying control system.
- OT Shield solution
- OT Shield is deployed as a bolt-on data-export layer on the legacy network's existing protocols (Modbus, UDP, BACnet), giving modern IT and cloud systems a live data feed without any change, patch, or re-certification of the legacy control system.
- Outcome
- Digital transformation achieved without disturbing validated control logic
- No re-certification cost for the existing PLC/SCADA platform
- Clear, low-risk migration path towards eventual modernisation
Safety Instrumented System (SIS) Event Logging
Process Safety & Compliance
- Challenge
- Process safety and compliance teams need SIS trip and event logs for incident investigation and regulatory reporting, but the SIS network is the most safety-critical zone in the plant and must never accept inbound connections.
- OT Shield solution
- OT Shield exports SIS event and trip logs one-way via Syslog/UDP file transfer to a compliance reporting server, giving safety engineers rapid access to forensic data without any external system ever reaching the SIS network.
- Outcome
- Faster incident investigation and root-cause analysis
- SIS network remains isolated per IEC 62443 zone/conduit principles
- Supports process safety compliance evidence and audits
Multi-Plant Data Aggregation for Corporate Reporting
Multi-Site Manufacturing Groups
- Challenge
- Manufacturing groups operating several plants need to aggregate production, quality and energy data centrally for corporate reporting and benchmarking, without bridging separate plant control networks together.
- OT Shield solution
- Each plant's OT Shield independently isolates its own control network while permitting production data to be aggregated and cross-analysed at the corporate IT/cloud layer, so visibility can be pooled centrally without ever connecting two OT networks directly.
- Outcome
- Group-wide production visibility without direct OT-to-OT connectivity
- Each plant retains independent, physically enforced isolation
- Supports benchmarking and centralised energy/quality reporting
Secure Remote Vendor Support Without Direct OT Access
OEM & Third-Party Support
- Challenge
- Equipment OEMs and system integrators often request remote access to plant data for diagnostics and warranty support, but granting inbound remote access to the control network is one of the most common causes of ICS breaches.
- OT Shield solution
- OT Shield provides OEMs and integrators with a one-way feed of the diagnostic data they need for remote support, entirely removing the need to grant any inbound remote access into the control network itself.
- Outcome
- Vendor support enabled without any inbound path into OT
- Eliminates a common root cause of third-party-linked ICS breaches
- Simplifies vendor access governance and audit
Compliance & Standards Alignment
The table below maps ChiefNET OT Shield capabilities to the standards and regulatory expectations most relevant to industrial operators.
| Framework / Requirement | Requirement Summary | How OT Shield Addresses It |
|---|---|---|
| IEC 62443 (Zones & Conduits) | Segment IACS into security zones connected by controlled conduits. | OT Shield functions as a physically-enforced conduit between zones with only one permitted direction of flow. |
| NIST SP 800-82 | Recommends unidirectional gateways at high-consequence OT/IT boundaries. | Hardware data diode directly implements the unidirectional gateway control NIST describes. |
| Purdue Model (ISA-95) | Defines controlled data flow between Level 3 control systems and Level 4 enterprise systems. | OT Shield enforces the Level 3.5 boundary as a one-way conduit with no reverse path. |
| CERT-In / Sectoral CERT Advisories | Maintain baseline security hygiene and incident reporting for critical/industrial infrastructure. | Reduces the ICS attack surface that leads to reportable incidents; simplifies audit evidence. |
| Cyber-Insurance & Supply-Chain Due Diligence | Demonstrate OT/IT segmentation as a condition of coverage or vendor qualification. | Provides a hardware-verifiable segregation control that is straightforward to evidence to insurers and customers. |
Business Value
| Business Driver | Impact of ChiefNET OT Shield |
|---|---|
| Production uptime | Removes the most common remote-attack vector into control systems, reducing risk of intrusion-driven shutdowns. |
| Audit and insurance readiness | Provides a hardware-verifiable segregation control that is straightforward to demonstrate to auditors and insurers. |
| Operational cost | Eliminates recurring OT firewall patch cycles and associated planned-outage windows for rule updates. |
| Industry 4.0 pace | Allows MES, cloud analytics and predictive maintenance initiatives to proceed without re-architecting or re-certifying control systems. |
| Multi-plant scalability | Centralised, zero-touch provisioning supports rollout across many plants from a single management platform. |
| Incident response | Rapid, low-risk access to historian, SIS and equipment logs speeds up root-cause analysis after an event. |
ChiefNET OT Shield vs. Traditional Firewalls
In industrial environments, where planned outages for patching are costly and unplanned downtime directly affects production, the distinction between rule-based and hardware-enforced isolation is a first-order design decision.
| Dimension | ChiefNET OT Shield | Traditional Firewall |
|---|---|---|
| Data directionality | One-way, physically enforced | Two-way, governed by software rules |
| Patch / maintenance burden | None – isolation is hardware, not firmware | Frequent patching, often needing outage windows |
| Misconfiguration risk | Not applicable – no rule set to misconfigure | Common cause of real-world ICS breaches |
| Resistance to remote exploitation | Near-total – no reverse path exists to exploit | Moderate; depends on rule hygiene and patch currency |
| Fit for production-critical control systems | Purpose-built for this class of asset | Adequate for IT; not ideal for critical ICS |
| Audit / compliance evidence | Physically demonstrable segregation | Requires ongoing rule and log review to evidence |
Technical Capability Snapshot
| Capability | Specification |
|---|---|
| Throughput | Up to 1 Gbps |
| Isolation | 100% one-way, optical / hardware-enforced physical air gap |
| Software exploit surface on reverse path | Zero – no reverse channel exists |
| ICS protocols supported | BACnet, Modbus, MQTT, OPC UA, industrial UDP (broadcast/multicast/anycast) |
| Data / file transfer | UDP file transfer, Syslog, HTTP PUT |
| Transport security | Encrypted VPN tunnel from RX side to monitoring/cloud endpoint |
| WAN connectivity (RX side) | Dual WAN with 4G/5G failover for uninterrupted delivery |
| Management | Cloud-hosted controller, zero-touch and pre-provisioning, fleet dashboards and alerting |
| Operating system | Hardened OS, minimised attack surface, no routine patch cycle required |
| Additional networking | Built-in SD-WAN for secure multi-site interconnection alongside OT isolation |
Deployment & Engagement Model
ChiefNET recommends a phased engagement for industrial deployments, allowing manufacturers to validate the solution on a representative line or plant before fleet-wide rollout.
Phase 1 – Assessment & Design
-
Site survey of target plant(s): control network topology, protocols in use, existing firewall/VPN posture.
-
Identification of required data points (PLC/DCS tags, historian exports, SIS logs) and target IT/cloud destinations.
-
Reference architecture and bill-of-materials finalised against IEC 62443 zone-and-conduit requirements.
Phase 2 – Pilot Deployment
-
OT Shield installed at one representative plant or line, configured for the identified protocols and data flows.
-
Validation of one-way data delivery, VPN transport and cloud dashboard visibility with plant operations teams.
-
Compliance walkthrough to confirm alignment with the organisation’s cybersecurity policy and applicable standards.
Phase 3 – Fleet Rollout (site-dependent)
-
Zero-touch provisioning used to scale deployment across remaining plants and lines.
-
Central SOC/NOC dashboards extended to provide fleet-wide monitoring and alerting.
-
Documentation and audit evidence packaged for compliance and insurance reviews.
Phase 4 – Ongoing Support
- ChiefNET provides device health monitoring, remote diagnostics support and periodic architecture reviews as monitoring and analytics needs evolve.
Conclusion
Industrial operators face a structural challenge: the same connectivity that enables Industry 4.0 initiatives also expands the attack surface of production-critical control systems. ChiefNET OT Shield resolves this tension directly – not by adding another rule set to manage, but by making the reverse path physically impossible.
Across discrete manufacturing, process industries and industrial utilities, the use cases in this document show a consistent pattern: operational data flows out for analytics, maintenance and compliance, while command-and-control risk is removed at the hardware level. For manufacturers balancing digital transformation against production uptime and safety requirements, that combination – visibility without exposure – is the foundation ChiefNET OT Shield is built to provide.